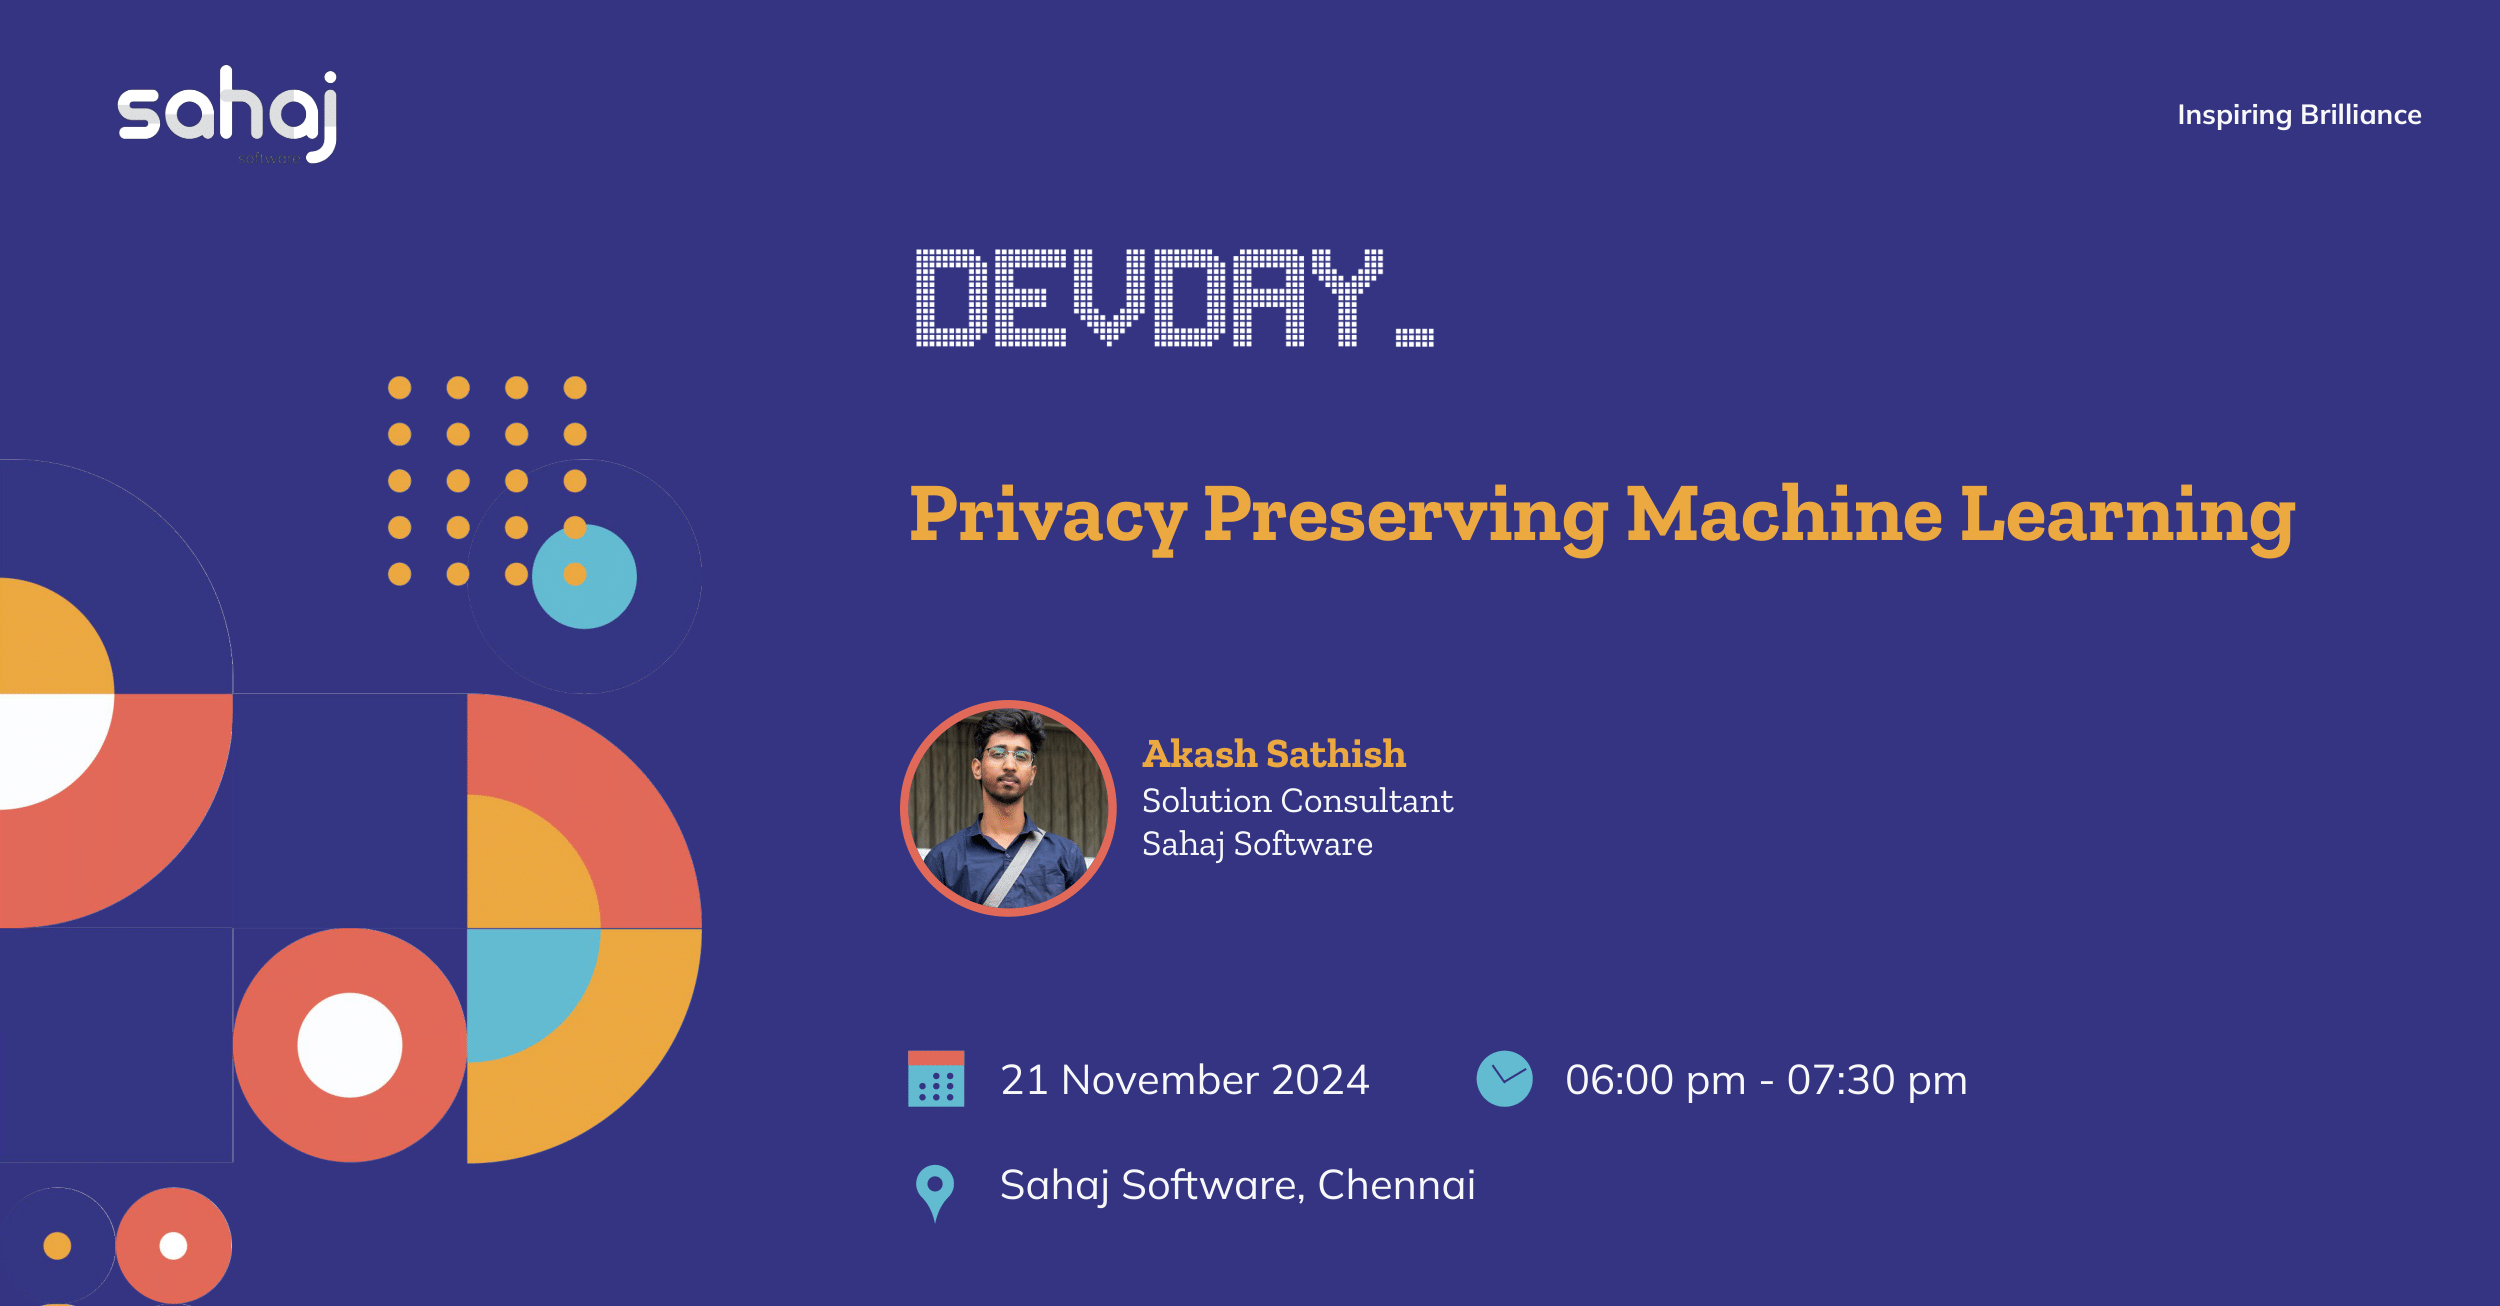
Machine learning is a double-edged sword—an innovation marvel yet a potential vault-cracker, holding secrets that we may not even realize we’re sharing. With every digital interaction, vast streams of data from our daily lives are quietly gathered, processed, and analyzed. But as models grow more advanced, a pressing question emerges: Is our data truly safe? Could these intelligent systems unwittingly expose private details, making them vulnerable to attacks?
Join us in exploring the fascinating world of privacy-preserving machine learning, where we’ll unravel how attackers might exploit models to extract personal data—and the cutting-edge techniques being developed to safeguard it. A basic understanding of machine learning and cryptography is helpful, but even newcomers will find value in this accessible session.
Agenda:
• Exploring the Vulnerabilities of Traditional Machine Learning in Sensitive Data Environments
• Homomorphic Encryption: Can We Truly Derive Insights Without Ever Decrypting Data?
• Differential Privacy: Safeguarding Individuals’ Privacy Within Massive Data Pools
• Federated Learning: The Rise of Distributed AI and Its Importance in Privacy-Preserved ML
• Secure Aggregation: Unlocking Privacy through Advanced Data Aggregation Protocols
• Practical Strategies for Integrating Privacy into Machine Learning Models
• The Future of AI: How Privacy-Preserving Technologies are Shaping Tomorrow’s Innovations